Get in Touch
![Managed Security Services]()
![people image]()
![hi ai]()
![house of x factor]()

![image]()
![bottom]()
The Threat Is Intelligent. So Is the Team Watching for It.
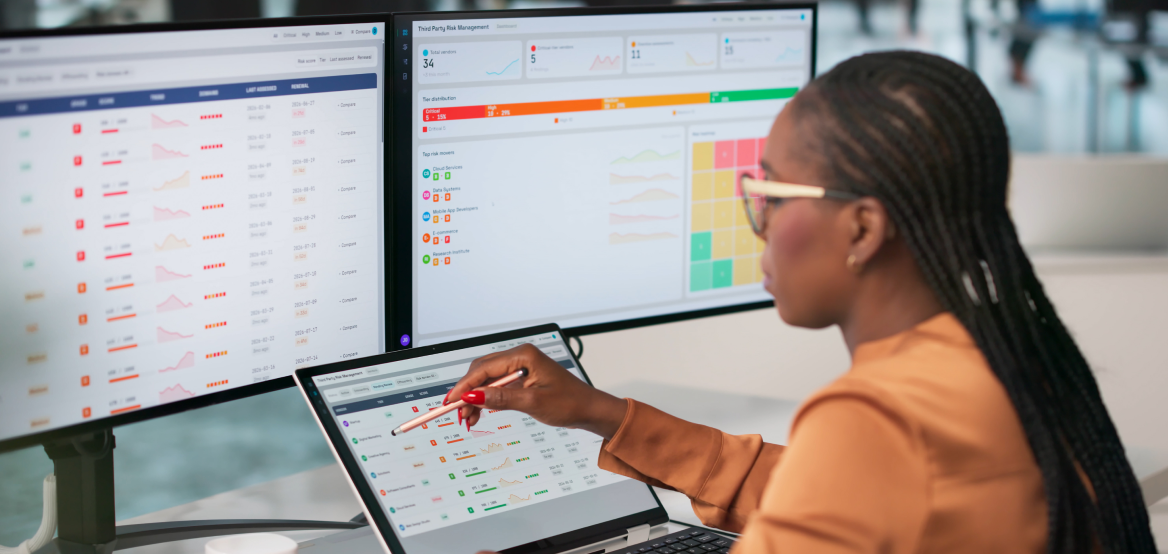
Threats are no longer random. They are targeted, adaptive and designed to hide inside the volume that overwhelms most security operations. The enterprises that stay protected are not the ones with the most alerts, they are the ones with the intelligence to separate signal from noise and the judgement to act before the threat lands. Xoriant runs SOC-as-a-Service that pairs AI-driven predictive analytics with expert human judgement, neutralising routine threats instantly and freeing analysts to focus on the ones that matter most.
Detection at AI Speed. Response at Human Precision.
Most security operations teams are not losing to sophisticated threats. They are losing to volume - buried in alerts generated faster than any team can process them, while the threats that matter move quietly through the noise. Scaling headcount addresses the symptom. It does not solve the signal problem. The answer is not more analysts. It is the right intelligence reaching the right analyst at the right moment.
Xoriant places AI at the service of human judgement, not in place of it. Our SOC specialists combine predictive analytics, SOAR automation and cloud-native telemetry to detect and resolve routine threats at machine speed, clearing the noise so experienced analysts can focus their precision exactly where it belongs: on the incidents that automation sees but only human ingenuity can resolve.
Overarching philosophy of HI/AI
House of Xfactors make it happen
How Can We Help ?
Capabilities That Form a Unified Cyber Defence Matrix
AI-Driven SOC-as-a-Service
Managed Detection, Response and XDR
Managed Infrastructure and Cloud Security
Managed GRC and Log Analytics
Managed Identity and Anomaly Detection
AI-Driven SOC-as-a-Service
AI-Driven SOC-as-a-Service
Cloud-native platforms and expert-led operations cut alert noise and improve prioritisation, delivering continuous monitoring without an in-house SOC.
Managed Detection, Response and XDR
Managed Detection, Response and XDR
Automated analytics combined with expert investigation accelerate breach detection, isolate threats faster, and reduce dwell time across the estate.
Managed Infrastructure and Cloud Security
Managed Infrastructure and Cloud Security
Scalable cloud security operations deliver continuous protection across hyperscalers, endpoints, and networks using adaptive, policy-driven enforcement.
Managed GRC and Log Analytics
Managed GRC and Log Analytics
SIEM and SOC integration enable continuous monitoring, centralised visibility, and audit-ready compliance across every regulatory framework in scope.
Managed Identity and Anomaly Detection
Managed Identity and Anomaly Detection
UEBA correlates access behaviour with risk signals, identifying insider threats and credential misuse before impact occurs anywhere in the estate.
Case Study
Fortifying Application Security for a B2B Data Provider Using the SSDLC Approach
Robust app security results in secured, compliant and risk-free apps.
Case Study
Fortifying the Banking Frontlines with Improved Network and Security
Automated device hardening from weeks to minutes without errors.
Case Study
Faster Big Data Testing and Migration with Metadata-driven Framework
60% Improved Delivery Efficiency Using Test Automation During Migration From SQL Server to Snowflake.
Accelerators
Built to Accelerate What Matters Most
Differentiators
Engineering at the Xoriant Scale
Behavioural Foresight
AI-driven SOC operations analyse behavioural patterns across users, endpoints, and workloads to detect intent, catching zero-day and evasive attacks early.
Autonomous Resilience
MDR and XDR with intelligent playbooks isolate, contain, and remediate incidents within seconds, handling routine alerts without analyst fatigue.
Intuition Amplified by Data
Correlated telemetry and threat intelligence help analysts uncover hidden attack paths that traditional tools miss, reducing noise and false positives.
Keeping You Updated



FAQ
Managed Security Services
What is SOC-as-a-Service and how does it strengthen enterprise security?
Xoriant provides cloud-native SOC operations, AI-driven analytics, automated response workflows, and expert security engineering to enhance visibility and improve operational resilience.
How do MDR and XDR services improve threat detection and response?
Xoriant integrates AI-powered detection models, correlation engines, SOAR automation, and cloud security telemetry to deliver faster containment and reduced MTTR across hybrid environments.
What is managed threat monitoring and why is it critical for modern enterprises?
Xoriant deploys full-stack observability, automated threat detection pipelines, ML-driven alerting, and security posture dashboards powered by platform engineering practices.
How do cloud security operations protect workloads across multi-cloud environments?
Xoriant integrates CSPM, CIEM, encryption frameworks, Zero Trust controls, and AIOps-driven telemetry to protect applications, data, and identities across all cloud environments.
What do vulnerability management services include?
Xoriant uses automated scanning, patch orchestration, risk scoring, and remediation analytics to maintain a strong security posture and reduce exploit risks enterprise-wide.
How does breach detection and response enhance security resilience?
Xoriant employs behavioural analytics, forensic investigation, threat intelligence integration, and automated containment workflows for rapid, coordinated incident response.
Start a Conversation about your next horizon